What is GitLab?
With GitLab, Security is built into the CI pipeline, out of the box. Every code commit is automatically scanned for security vulnerabilities in your code and its dependencies. Actionable results are delivered to the developer in their native workflow for rapid remediation.
Company Details
Need Assistance?
We're here to help you with understanding our reports and the data inside to help you make decisions.
Get AssistanceGitLab Ratings
Real user data aggregated to summarize the product performance and customer experience.
Download the entire Product Scorecard
to access more information on GitLab.
Product scores listed below represent current data. This may be different from data contained in reports and awards, which express data as of their publication date.
91 Likeliness to Recommend
98 Plan to Renew
88 Satisfaction of Cost Relative to Value
1
Since last award
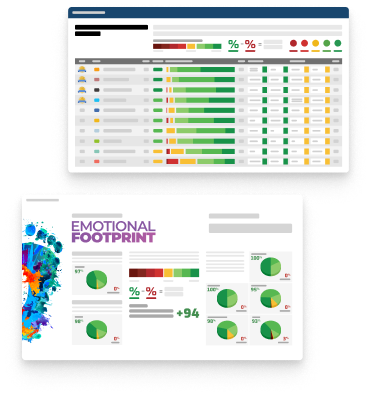
Emotional Footprint Overview
Product scores listed below represent current data. This may be different from data contained in reports and awards, which express data as of their publication date.
+98 Net Emotional Footprint
The emotional sentiment held by end users of the software based on their experience with the vendor. Responses are captured on an eight-point scale.
How much do users love GitLab?
Pros
- Helps Innovate
- Reliable
- Performance Enhancing
- Client Friendly Policies
How to read the Emotional Footprint
The Net Emotional Footprint measures high-level user sentiment towards particular product offerings. It aggregates emotional response ratings for various dimensions of the vendor-client relationship and product effectiveness, creating a powerful indicator of overall user feeling toward the vendor and product.
While purchasing decisions shouldn't be based on emotion, it's valuable to know what kind of emotional response the vendor you're considering elicits from their users.
Footprint
Negative
Neutral
Positive
Feature Ratings
SDLC Integration
Vulnerability Scanning
Static Application Security Testing (SAST)
Container Security Testing
Risk Scoring
Policy Engine and Enforcements
False Positive Remediation
Integrated Development Environment (IDE) plug-in
Dynamic Application Security Testing (DAST)
Software Composition Analysis (SCA)
Interactive Application Security Testing (IAST)
Vendor Capability Ratings
Business Value Created
Ease of Data Integration
Product Strategy and Rate of Improvement
Ease of Implementation
Breadth of Features
Vendor Support
Availability and Quality of Training
Quality of Features
Ease of IT Administration
Ease of Customization
Usability and Intuitiveness
GitLab Reviews
Ubaidul H.
- Role: Information Technology
- Industry: Technology
- Involvement: IT Leader or Manager
Submitted Sep 2026
Powerful Integrated Platform for Modern DevSecOps
Likeliness to Recommend
What differentiates GitLab from other similar products?
The main advantage of GitLab is its single-platform approach that covers the whole DevSecOps cycle. It provides extensive built-in possibilities in such areas as source code management, CI/CD, security testing, vulnerability management, and collaboration. This feature allows reducing the number of external tools involved in the process and provides a common interface for DevOps, Security, and Operations teams.
What is your favorite aspect of this product?
My favorite aspect is the way GitLab brings development, CI/CD, and security capabilities together in one platform. Having security scanning and vulnerability management integrated directly into the development workflow makes it easier to identify and address issues without constantly switching between different tools.
What do you dislike most about this product?
The main drawback is that GitLab can feel complex at first, especially with the number of features and configuration options available. Setting up and fine-tuning security scanning, CI/CD pipelines, and policies can require some time and technical expertise.
What recommendations would you give to someone considering this product?
I would suggest assessing this GitLab product based on the specific needs of your organization. It may streamline a lot of processes and make the development, CI/CD, and security tasks much more organized. However, there might be a need to spend some time configuring the system and studying its many functions. A POC or trial may be a good idea for you to see if it suits your team and operations.
Pros
- Continually Improving Product
- Reliable
- Trustworthy
- Saves Time
Please tell us why you think this review should be flagged.
Nistha J.
- Role: Information Technology
- Industry: Other
- Involvement: End User of Application
Submitted Mar 2026
Unified platform for release management
Likeliness to Recommend
What differentiates GitLab from other similar products?
integrates source code management cl cd and security into a single platform.
What is your favorite aspect of this product?
ability to manage the end to end release lifecycle on a single platform.
What do you dislike most about this product?
initial setup and pipeline configuration can be complex.
What recommendations would you give to someone considering this product?
adopt it as the primary devops platform for release management.
Pros
- Helps Innovate
- Reliable
- Saves Time
- Fair
Please tell us why you think this review should be flagged.
Mary W.
- Role: Information Technology
- Industry: Technology
- Involvement: End User of Application
Submitted Feb 2026
Confident deployment with secure code
Likeliness to Recommend
What differentiates GitLab from other similar products?
GitLab unifies application security testing directly with the CI/CD pipeline. Unlike standalone security tools, it integrates into the same workflow used for development and deployment. This unified approach reduces friction, ensures security is part of DevOps from the start, and provides actionable reports within the same interface.
What is your favorite aspect of this product?
The major significant side of GitLab for application security testing is its seamless integration into the DevOps workflow. I don’t need to switch between tools or environments to identify vulnerabilities, as everything is built into the CI/CD pipeline. The dashboards and merge request alerts make it easy to track and prioritize vulnerabilities.
What do you dislike most about this product?
GitLab’s application security testing is well-integrated and effectively supports maintaining secure development workflows.
What recommendations would you give to someone considering this product?
One should utilize its automated security scans, merge request alerts, and dashboards to identify and fix vulnerabilities early, ensuring faster and safer software delivery.
Pros
- Reliable
- Unique Features
- Effective Service
- Inspires Innovation
Please tell us why you think this review should be flagged.


Get Instant Access<br>to this Report
Get Instant Access
to this Report
Unlock your first report with just a business email. Register to access our entire library.
© 2026 SoftwareReviews.com. All rights reserved.