
What is SonarQube?
SonarQube is the leading tool for continuously inspecting the Code Quality & Security of your codebases and guiding development teams during Code Reviews. Covering 27 programming languages, while pairing-up with your existing software pipeline, SonarQube provides clear remediation guidance for developers to understand and fix issues and ultimately deliver better and safer software. With over 170k deployments helping small development teams as well as global organizations, SonarQube provides the means for all teams and companies around the world to own and impact their Code Quality.
Company Details
Need Assistance?
We're here to help you with understanding our reports and the data inside to help you make decisions.
Get AssistanceSonarQube Ratings
Real user data aggregated to summarize the product performance and customer experience.
Download the entire Product Scorecard
to access more information on SonarQube.
Product scores listed below represent current data. This may be different from data contained in reports and awards, which express data as of their publication date.
90 Likeliness to Recommend
100 Plan to Renew
82 Satisfaction of Cost Relative to Value
1
Since last award
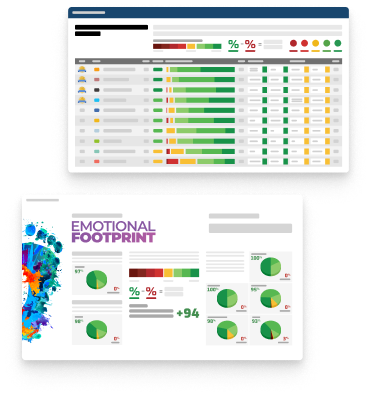
Emotional Footprint Overview
Product scores listed below represent current data. This may be different from data contained in reports and awards, which express data as of their publication date.
+94 Net Emotional Footprint
The emotional sentiment held by end users of the software based on their experience with the vendor. Responses are captured on an eight-point scale.
How much do users love SonarQube?
Pros
- Transparent
- Caring
- Over Delivered
- Appreciates Incumbent Status
How to read the Emotional Footprint
The Net Emotional Footprint measures high-level user sentiment towards particular product offerings. It aggregates emotional response ratings for various dimensions of the vendor-client relationship and product effectiveness, creating a powerful indicator of overall user feeling toward the vendor and product.
While purchasing decisions shouldn't be based on emotion, it's valuable to know what kind of emotional response the vendor you're considering elicits from their users.
Footprint
Negative
Neutral
Positive
Feature Ratings
Vulnerability Scanning
Policy Engine and Enforcements
Static Application Security Testing (SAST)
Mobile Application Security Testing
SDLC Integration
Dynamic Application Security Testing (DAST)
Interactive Application Security Testing (IAST)
Risk Scoring
Integrated Development Environment (IDE) plug-in
Container Security Testing
False Positive Remediation
Vendor Capability Ratings
Ease of Data Integration
Business Value Created
Ease of Implementation
Breadth of Features
Vendor Support
Product Strategy and Rate of Improvement
Quality of Features
Ease of Customization
Availability and Quality of Training
Usability and Intuitiveness
Ease of IT Administration
SonarQube Reviews

Chiesa B.
- Role: Information Technology
- Industry: Insurance
- Involvement: End User of Application
Submitted Mar 2025
My preferred tool for code quality analysis .
Likeliness to Recommend
What differentiates SonarQube from other similar products?
I love and appreciate that Sonarqube integrates with the CI/CD ( continuous integration and continuous deployment ) infrastructure on Gitlab. This comes with a whole lot of benefit when developing software , including helping to comply with best coding standards and practices, it also helps with facilitating collaboration between developers and reviewers in the process of developing software. Of importance is the early detection of security risks within the development process, even before code is passed into the repository.
What is your favorite aspect of this product?
Among the main strength of Sonarqube is its support for different programming languages. This makes Sonarqube the unified tool to use for the purpose of analyzing code quality, regardless of the programming language in which the code was written.
What do you dislike most about this product?
In situations where we have tried to reuse legacy codebases, we have noticed that Sonarqube easily gets overwhelmed by the inherent technical debt and problems which are common on legacy codebases. Of importance, is its tendency to generate a lot of false positives when working on Legacy codes.
What recommendations would you give to someone considering this product?
As far as enterprise level code management is concerned , I think Sonarqube is the tool I recommend because of its rule based analysis and its support for a variety of programming languages. It is important though, that it is setup and customized properly.
Pros
- Reliable
- Performance Enhancing
- Enables Productivity
- Security Protects
Please tell us why you think this review should be flagged.

Jeemish M.
- Role: Information Technology
- Industry: Technology
- Involvement: IT Leader or Manager
Submitted Jul 2023
Enterprise scale SAST scans at zero cost !!
Likeliness to Recommend
What differentiates SonarQube from other similar products?
Ease of implementation and support for most common technology stacks like java, Js, .net, python, groovy, etc for SAST scans
What is your favorite aspect of this product?
Minimalistic UI and multiple technology stack support
What do you dislike most about this product?
Requires a lot of manual setup and configuration for maintenance
What recommendations would you give to someone considering this product?
Must have for implementing automated SAST scans at enterprise scale
Pros
- Helps Innovate
- Reliable
- Performance Enhancing
- Respectful
Please tell us why you think this review should be flagged.

Emily L.
- Role: Information Technology
- Industry: Technology
- Involvement: End User of Application
Submitted Nov 2026
Strengthening code quality and security
Likeliness to Recommend
What differentiates SonarQube from other similar products?
The way SonarQube brings code quality assessment and security analysis together within the development workflow, makes it a compelling option in the AST market. Moreover, its potential to detect vulnerabilities and highlight maintainability concerns gives us a broader understanding of our codebase. Integration with CI/CD pipelines also allows us to address issues before they reach production.
What is your favorite aspect of this product?
I find its code analysis process impressive as it highlights problems at the point where we can actually address them. The detailed issue descriptions, security hotspots, and quality gate checks provide clear direction during code reviews. I also like how dashboards help track technical debt and maintain consistent coding standards across projects.
What do you dislike most about this product?
The initial configuration takes some effort, especially when setting up project-specific quality profiles. Large codebases also generate numerous findings, requiring additional filtering and prioritization before we can focus on the most critical security concerns.
What recommendations would you give to someone considering this product?
My fair recommendation would be to configure security rules according to your development standards, integrate SonarQube into CI/CD pipelines, and review findings regularly to maintain code quality.
Pros
- Helps Innovate
- Continually Improving Product
- Performance Enhancing
- Enables Productivity
Please tell us why you think this review should be flagged.


Get Instant Access<br>to this Report
Get Instant Access
to this Report
Unlock your first report with just a business email. Register to access our entire library.
© 2026 SoftwareReviews.com. All rights reserved.